Pwdly scored 5.0/10. Here’s the honest update.
iTechGuides ranked Pwdly #41 of 90 password managers with a 5.0/10 score. Here is what that milestone means, why development has slowed, and why deliberate progress matters in security software.
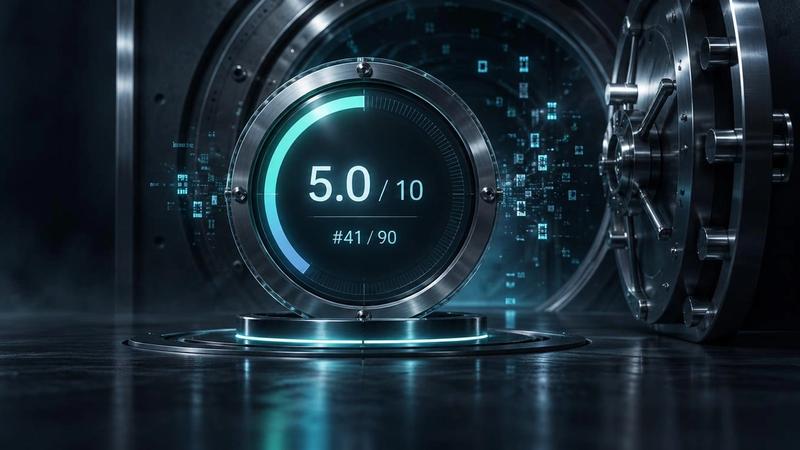
Pwdly has been reviewed by iTechGuides. The result: 5.0 out of 10, and a current position of number 41 in a field of 90 password managers.
That is not the sort of score most company blogs put in 64-point type. So naturally, we are going to talk about it.
The listing, marked as fact-checked on 20 September 2026, is based on researched product facts rather than hands-on testing. You can read the full iTechGuides page here.
A perfectly average score — and a useful outside view
Five out of ten is not an award. Number 41 is not a podium. We are not going to add a laurel wreath to the homepage or quietly round the score up in a press release.
But being included matters. Pwdly is now sitting in a public catalogue alongside products with much larger teams, longer histories and considerably louder marketing departments. An independent publisher has researched it, documented it and placed it in the category. For a small, focused product, that is a real milestone — even when the number attached to it is exactly in the middle.
The score is useful for another reason: it is a snapshot of how Pwdly looks from the outside. It does not measure every design decision we care about, and it was not produced from a hands-on security audit. It is still a fair reminder that there is plenty left to improve.
The honest product update
Feature development has slowed. Other commitments have needed more of my time, and pretending otherwise would be the least Pwdly thing we could do.
Pwdly has not disappeared, though. I still use it every day. My team uses it every day. A small group of other teams continue to trust it with the shared credentials and two-factor codes that keep their work moving.
That daily use matters more than a carefully worded status update. It means the product remains exposed to real browsers, real logins, real team changes and all the unglamorous edge cases that appear when software has to work rather than demo well.
Recent work reflects that reality: fixing expired extension sessions, detecting login forms that bypass normal submit events, and making newly saved credentials appear immediately. None of those changes makes for a dramatic new category on a comparison chart. All of them make the product better for the people already relying on it.
Why slower development can be a feature in a password manager
“Move fast and break things” is a questionable philosophy when the thing being broken stores the keys to everything else.
A password manager sits in an awkward category. People reasonably want new features, but every new feature expands the amount of code, behaviour and data flow that has to be understood and defended. Speed is not automatically progress. Sometimes the responsible decision is to leave a stable system alone until a change is worth its security cost.
Slower development gives us room to ask boring but important questions before shipping:
- Does this change preserve the zero-knowledge boundary? Sensitive values must still be encrypted in the browser before they leave the device.
- Does it create a new recovery path or privileged shortcut? Convenient back doors remain back doors, even when they are labelled as support tools.
- Does it help teams do their actual work? A smaller, dependable workflow is more valuable than a crowded feature list nobody trusts.
- Can we maintain it properly? Shipping a security feature is a commitment to keep understanding it long after launch day.
This is not an argument that slow software is automatically secure. Neglect is not a security model, and a lack of releases is not evidence of careful engineering. Vulnerabilities, browser changes and broken workflows still need prompt attention. Maintenance has to continue.
It is simply an argument against treating release volume as the only sign of a healthy password manager. Stability, restraint and fixing the less glamorous problems count too.
What happens next
There is no invented quarterly roadmap to reveal here, and no promise that Pwdly will suddenly ship a dozen headline features. Development will continue at a pace that fits the time available and the responsibility of changing security software.
The priorities remain straightforward: keep the core dependable, fix real problems, improve the experience where it creates genuine value, and never weaken the architecture simply to tick a box.
So yes: 5.0 out of 10. Number 41 of 90. We are pleased to be on the list, clear-eyed about the distance left to travel, and still using the product every day.
Slowly is not the same as standing still.